Every Windows Remote Desktop session is authenticated either with Kerberos or with NTLM, and the client makes that choice silently. A user who connects through JumpServer has no way to tell which protocol was used. For teams that have retired NTLM, or that need to show an auditor a real Kerberos ticket exchange, that ambiguity is not acceptable.
This guide covers how to make JumpServer RDP sessions authenticate against Active Directory with Kerberos, from asset configuration to KDC discovery, and how to prove the result on the target machine. JumpServer is an open source privileged access management platform, so the same gateway that records sessions also decides how each RDP logon is authenticated. The steps below apply to JumpServer v4.10.x-ee; the logic holds on other versions, although component image versions differ.
What You Will Learn
- Which prerequisites decide whether Kerberos is possible at all
- How RDP negotiates Kerberos or NTLM through CredSSP and SPNEGO
- Two ways to let the Razor client discover the KDC from inside Docker
- How to confirm with Windows event 4624 that Kerberos was really used
- What fails silently, and how to diagnose it
Why RDP Sessions Fall Back to NTLM
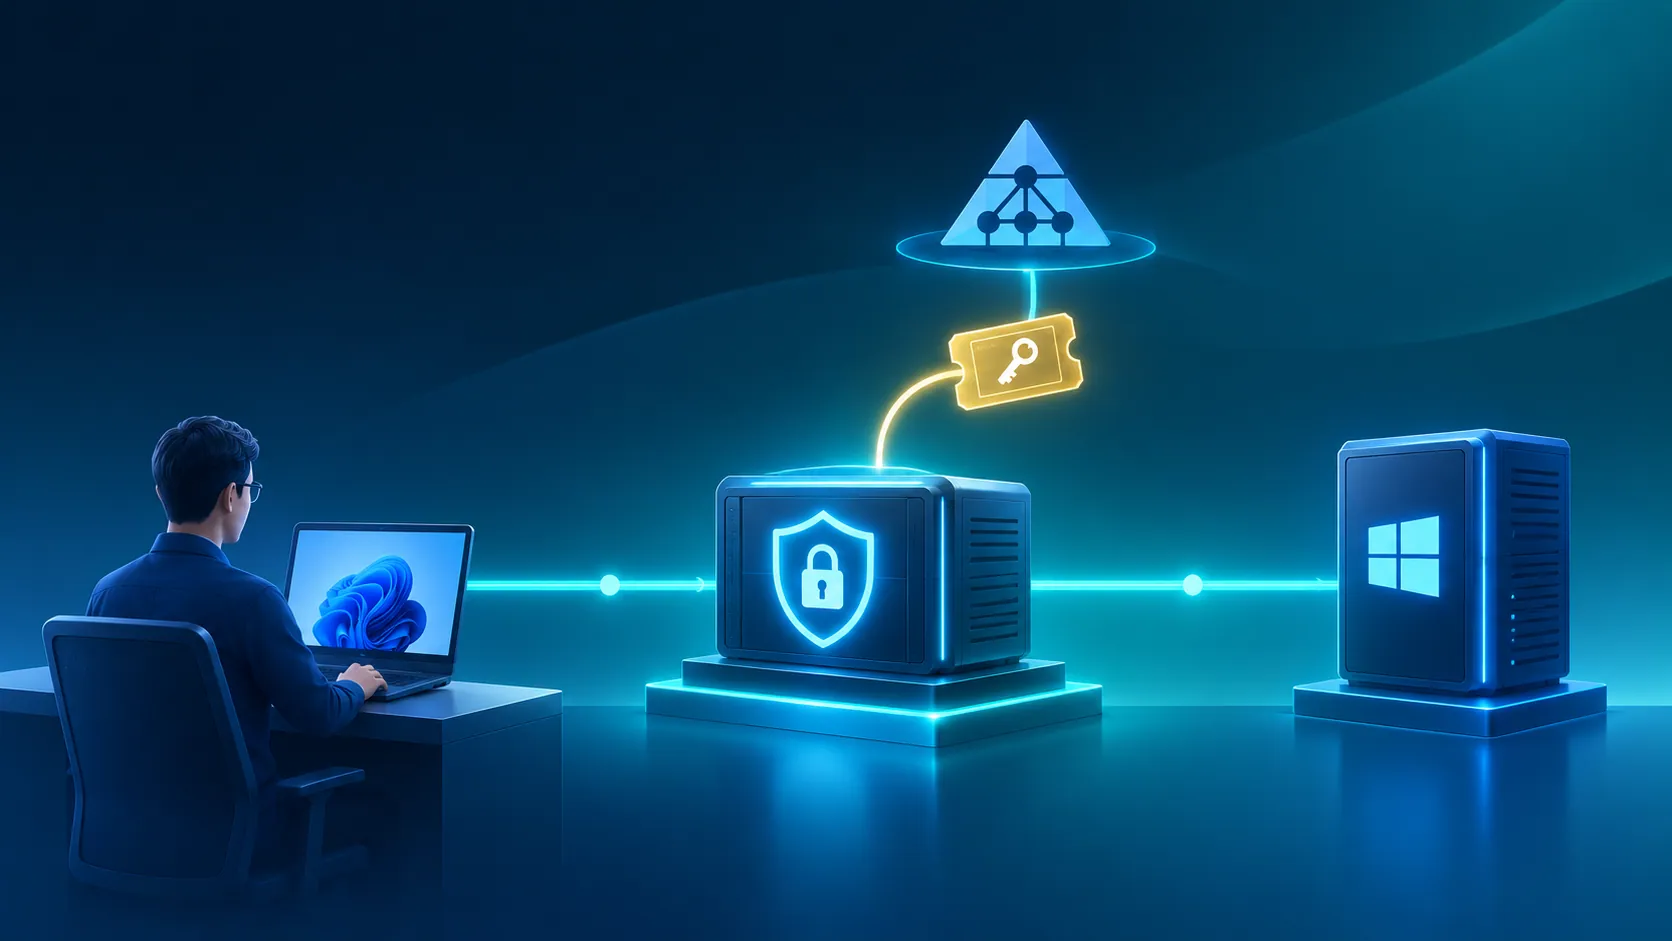
Kerberos needs a service ticket for TERMSRV/<FQDN> issued by a Key Distribution Center. If any link in that chain is missing, the client does not fail: it falls back to NTLM and the session still succeeds. That silent downgrade is why “it connects” proves nothing about the protocol. A bastion host that records every session can still be passing NTLM credentials underneath.
As of v4.10.16-lts, only Razor, the native client, can authenticate with Kerberos. Lion, the web terminal, still uses NTLM because it ships FreeRDP 2.x, and FreeRDP only gained Kerberos support in the 3.x line.
Kerberos is not available in any of these cases:
- The target host belongs to a workgroup, so no KDC exists
- The asset is addressed by IP instead of a FQDN
- The account is local rather than a domain account
- The session is opened through Lion instead of Razor
Prerequisites for Kerberos Authentication
Every item below must hold. A single missing item causes a fallback to NTLM or a failed logon.
| Requirement | Detail |
|---|---|
| AD domain | The target Windows host is domain-joined, so a KDC exists and the HOST and TERMSRV SPNs are registered |
| FQDN address | The asset address is a FQDN such as host.example.com, never an IP. An IP has no SPN and always falls back to NTLM |
| Realm in account | The account is [email protected] (UPN, preferred) or DOMAIN\user. A bare username carries no realm |
| Client | The session is opened through Razor, not through Lion |
| Network | Razor can reach the KDC on port 88, both TCP and UDP |
| Clock | Skew between client, KDC and target stays under 5 minutes |
How JumpServer Decides Between Kerberos and NTLM
RDP uses Network Level Authentication through CredSSP, which negotiates Kerberos or NTLM inside SPNEGO. Razor acts as the client, so it must be able to obtain a TERMSRV/<FQDN> ticket. When it cannot reach a KDC, or when the account carries no realm, NTLM is used and nothing is logged as an error.
The evidence lives on the target, in the Windows Security log: event 4624 with LogonType 3. AuthenticationPackageName reads Kerberos or NTLM, and LmPackageName separates NTLMv1 from NTLMv2. The LogonType 10 record describes the session shell rather than the logon, so it is not evidence either way.
Step 1 Create the Asset and the Domain Account
In JumpServer, open Assets and create a Windows asset. Set the address to the FQDN, for example win2019.example.com, and the protocol to RDP on port 3389. Set the account username to [email protected], or to EXAMPLE\user if you prefer the down-level form.
Step 2 Let Razor Discover the KDC
The Razor container ships without a krb5.conf file and resolves DNS through the Docker embedded resolver. That resolver knows nothing about the AD _kerberos SRV records, so Razor finds no KDC, fails without an error, and falls back to NTLM. Choose one of the two options below.
Option A Point Razor at the AD DNS Server
This option is recommended because it mirrors how a domain-joined Windows client behaves. Edit compose/razor.yml under the JumpServer install directory and add dns: to the razor service:
services:
  razor:
    container_name: jms_razor
    hostname: jms_razor
    dns:                      # add
      - 10.1.14.240           # AD DNS, usually the domain controller
    ...
Docker’s embedded resolver at 127.0.0.11 still resolves container names and forwards every other query to AD DNS. The _kerberos._udp and _kerberos._tcp SRV records resolve, and FreeRDP 3 discovers the KDC automatically. No krb5.conf is required. The AD DNS server must hold those SRV records and must have forwarders configured, otherwise Razor stops resolving external names.
Option B Mount a krb5.conf File
Use this option when changing Razor DNS is not acceptable, or when the KDC must be pinned to a specific address. Place the file on a persistent host path. The template is in the appendix; dns_lookup_kdc = false plus an explicit kdc entry are the essential lines.
cp krb5.conf /opt/jumpserver/krb5.conf
Add the read-only mount to the razor service:
    volumes:
      - ${VOLUME_DIR}/razor/data:/opt/razor/data
      - ${CONFIG_DIR}/nginx/cert:/opt/razor/cert
      - /opt/jumpserver/krb5.conf:/etc/krb5.conf:ro   # add
Step 3 Open Port 88 Between Razor and the KDC
Allow TCP and UDP 88 from the Razor host to the domain controller. Kerberos attempts UDP first and then TCP, so opening only one of the two produces intermittent failures. Verify from inside the container:
docker exec jms_razor bash -c 'timeout 3 bash -c ">/dev/tcp/10.1.14.240/88" && echo TCP88-OPEN'
Step 4 Verify That Kerberos Is Actually Used
Connect to the FQDN asset with the domain account through the client, then inspect event 4624 on the target:
Get-WinEvent -FilterHashtable @{LogName='Security'; Id=4624; StartTime=(Get-Date).AddMinutes(-15)} |
  ForEach-Object {
    $x = [xml]$_.ToXml(); $d = @{}
    $x.Event.EventData.Data | ForEach-Object { $d[$_.Name] = $_.'#text' }
    if ($d['LogonType'] -eq '3') {
      [pscustomobject]@{
        Time    = $_.TimeCreated
        Package = $d['AuthenticationPackageName']
        Account = $d['TargetUserName']
        Source  = $d['IpAddress']
      }
    }
  } | Sort-Object Time -Descending | Format-Table -AutoSize
A Package value of Kerberos confirms that the session used Kerberos. Any other value means NTLM, even though the session succeeded. Once Kerberos is in place, the session itself is still recorded as before, so session recordings complete the audit trail alongside the logon evidence.
Troubleshooting Kerberos Authentication Failures
| Symptom | Cause | Fix |
|---|---|---|
| 4624 still shows NTLM | The session went through Lion, used an IP address, or the account carries no realm | Use Razor, the FQDN and user@realm |
| 4624 still shows NTLM with Razor, a FQDN and a domain account | Razor cannot find the KDC and falls back silently | Apply Option A or B, then confirm port 88 |
| Razor log reports Cannot find KDC for realm | No krb5.conf and no _kerberos SRV record in DNS |
Same as above |
| KRB_AP_ERR_SKEW | Clock skew above 5 minutes | Align every host to NTP |
| External names stop resolving after Option A | Razor DNS now points at AD DNS, which has no forwarders | Add forwarders to AD DNS |
| A workgroup host always uses NTLM | No domain, therefore no KDC | Join the host to the domain first |
Operational Cautions
- A successful connection does not prove Kerberos. Razor degrades to NTLM silently, so event 4624 is the only reliable evidence.
jmsctl upgradeoverwrites compose files. Re-apply therazor.ymlchanges after every upgrade, or the DNS setting and the volume mount disappear.- Lion support depends on FreeRDP 3.x, which arrives with Guacamole 1.6.0 or later. Until then, Lion stays on NTLM.
- To prove Kerberos by force, temporarily set Network security: Restrict NTLM: Incoming NTLM traffic to Deny all on the target. If the session still connects, it is using Kerberos. Keep console or out-of-band access available, or you will lock yourself out.
- Kerberos authenticates the logon, it does not harden the protocol itself. Pair it with the checks in RDP signing and encryption if the baseline requires more than identity assurance.
Using a Windows AD Domain Controller as the KDC
A Windows domain controller needs almost nothing extra: AD DS provides the KDC, and AD-integrated DNS already holds the SRV records. Configure DNS forwarders so member hosts can resolve external names.
Join the Target Host
# Point the NIC at AD DNS
Set-DnsClientServerAddress -InterfaceIndex <idx> -ServerAddresses <AD_DNS_IP>
# Join the domain and restart
Add-Computer -DomainName example.com -Credential (Get-Credential EXAMPLE\Administrator) -Restart
# After restart: enable RDP with NLA and allow the account
Set-ItemProperty 'HKLM:\System\CurrentControlSet\Control\Terminal Server' -Name fDenyTSConnections -Value 0
Set-ItemProperty 'HKLM:\System\CurrentControlSet\Control\Terminal Server\WinStations\RDP-Tcp' -Name UserAuthentication -Value 1
Enable-NetFirewallRule -DisplayGroup 'Remote Desktop'
Add-LocalGroupMember -Group 'Remote Desktop Users' -Member 'EXAMPLE\rdpuser'
Domain members sync time with the domain controller through the Windows Time service, which normally keeps the skew under 5 minutes.
Create the Account for JumpServer
New-ADUser -Name rdpuser -UserPrincipalName [email protected] `
  -AccountPassword (Read-Host -AsSecureString) -Enabled $true
Use [email protected], or EXAMPLE\rdpuser, as the asset account in JumpServer.
SPN Registration Needs No Manual Step
Domain members register HOST and TERMSRV SPNs automatically, and the Windows KDC maps TERMSRV to HOST, so TERMSRV/<fqdn> needs no manual entry. To confirm on a domain machine:
setspn -L <COMPUTERNAME>
setspn -Q TERMSRV/host.example.com
Hardening Is Optional
Either configure the Network security: Restrict NTLM policies through GPO, or add the account to the Protected Users group, which enforces Kerberos and blocks weak authentication. FreeRDP 3 supports that scenario. Protected Users has side effects, including no delegation and no NTLM or cached logon, so agree the change with the application owner before applying it.
Frequently Asked Questions
Does JumpServer support Kerberos in the Web Terminal?
Not yet. Lion, the web terminal, depends on FreeRDP 2.x, which has no Kerberos support. Kerberos RDP is available through Razor, the native client. Lion support will follow once the bundled FreeRDP reaches 3.x, which ships with Guacamole 1.6.0 and later.
Why Does the Session Still Connect When Kerberos Fails?
Because CredSSP treats Kerberos as the preferred mechanism, not a required one. When no ticket can be obtained, the client negotiates NTLM and the logon completes. Nothing surfaces in the JumpServer UI, which is why the target event log is the only trustworthy check.
Do I Need to Register the TERMSRV SPN Manually?
In a standard AD environment, no. Domain-joined computers register their own SPNs, and the KDC maps TERMSRV to HOST. Manual registration is only needed when the service runs under a dedicated account, or when a computer object has been reset without re-registering.
Will the Razor Configuration Survive an Upgrade?
No. jmsctl upgrade replaces the compose files, so the dns: entry or the krb5.conf mount has to be re-applied afterwards. Treat the change as part of the upgrade checklist and verify event 4624 again after each upgrade.
Appendix The krb5.conf Template
[libdefaults]
    default_realm = EXAMPLE.COM
    dns_lookup_realm = false
    dns_lookup_kdc = false
    rdns = false
    forwardable = true
[realms]
    EXAMPLE.COM = {
        kdc = 10.1.14.240
        admin_server = 10.1.14.240
    }
[domain_realm]
    .example.com = EXAMPLE.COM
    example.com = EXAMPLE.COM
To try the workflow end to end, the Community Edition is free for up to 5,000 assets and can be downloaded in minutes. The feature overview lists the protocols and audit capabilities that the Enterprise Edition adds on top.