JumpServer v5.1.1 Release Notes
JumpServer v5.1.1 hardens persistent write protection in high availability deployments, tightens RDP applet host deployment around NLA, and fixes replication and credential recovery issues in clustered environments.
Insights on privileged access management, cybersecurity, and open-source security.
JumpServer v5.1.1 hardens persistent write protection in high availability deployments, tightens RDP applet host deployment around NLA, and fixes replication and credential recovery issues in clustered environments.
JumpServer v4.10.20-lts released: editable search conditions, Oracle password changes with the REPLACE clause, SYSDBA connections, larger job argument limits, and stronger validation for login callbacks and asset addresses.
JumpServer v5.1.0 rebuilds the KoKo and Tinker components, adds Windows PowerShell WinRM and Dameng database Web CLI support, and introduces AI-assisted command filter rules, tab groups, and batch download of session recordings.
JumpServer V5 adds a built-in browser to its native client, so operators open web dashboards and admin consoles directly, with no Windows relay host to stand up.
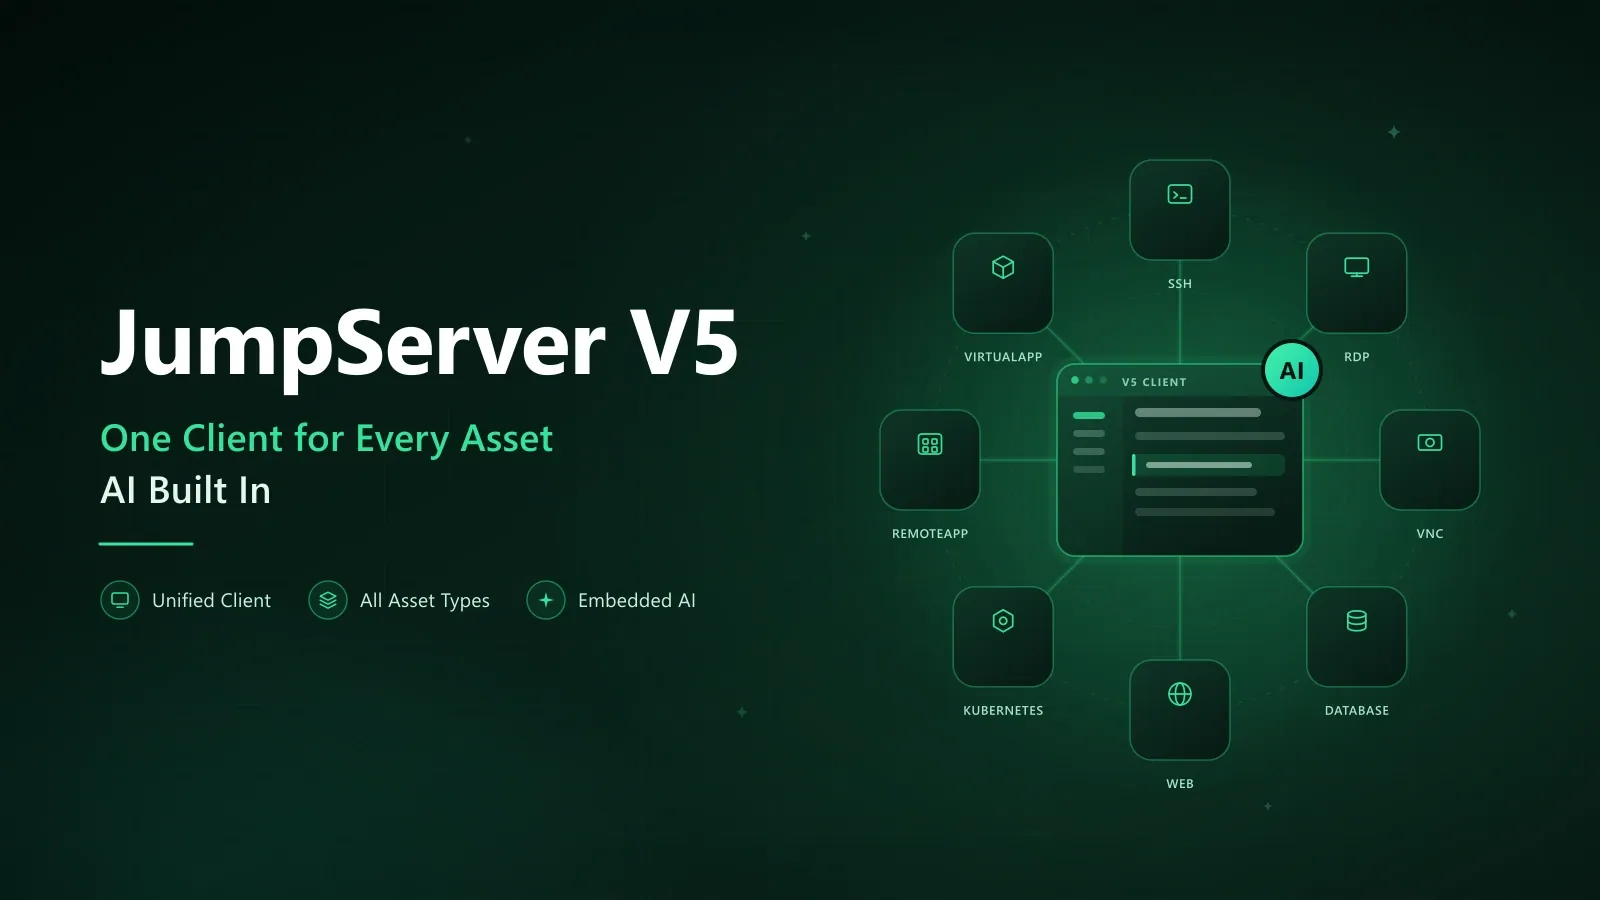
JumpServer v5.0.0 has arrived. V5 delivers a rebuilt native client that reaches SSH, RDP, VNC, databases, Web sites, Kubernetes, RemoteApp, and VirtualApp through one interface, and embeds AI in the bastion host for command recommendations, risk alerts, and automated audit reports.
A step-by-step guide to managing AWS IAM accounts and opening the AWS Management Console through JumpServer, with automated account discovery, password rotation, and verification on a custom AWS Console platform.
What is BeyondTrust? A guide to its identity security platform, product portfolio and limits, plus how JumpServer compares as an open-source PAM alternative.
KOTL is a new component shipped in JumpServer v4.10.19 LTS that gives administrators a built-in visual console for operating and maintaining the JumpServer platform itself, from network, domain, and disk settings to encrypted backups, container lifecycle, and live application logs.
JumpServer security advisory JS-2026.09.09: an improper API filtering vulnerability (GHSA-6rp5-ff2m-qfrm, High, CVSS 8.8) lets any authenticated user retrieve administrator Access Keys by appending a query parameter. Affects V3 >= v3.7.0 and < v3.10.23 LTS, and V4 >= v4.0.0 and < v4.10.19 LTS. Upgrade or apply the Nginx workaround immediately.