
Connecting to Web Assets in JumpServer V5: Built-in Browser, No Windows Host Required
JumpServer V5 adds a built-in browser to its native client, so operators open web dashboards and admin consoles directly, with no Windows relay host to stand up.
Insights on privileged access management, cybersecurity, and open-source security.
JumpServer V5 adds a built-in browser to its native client, so operators open web dashboards and admin consoles directly, with no Windows relay host to stand up.
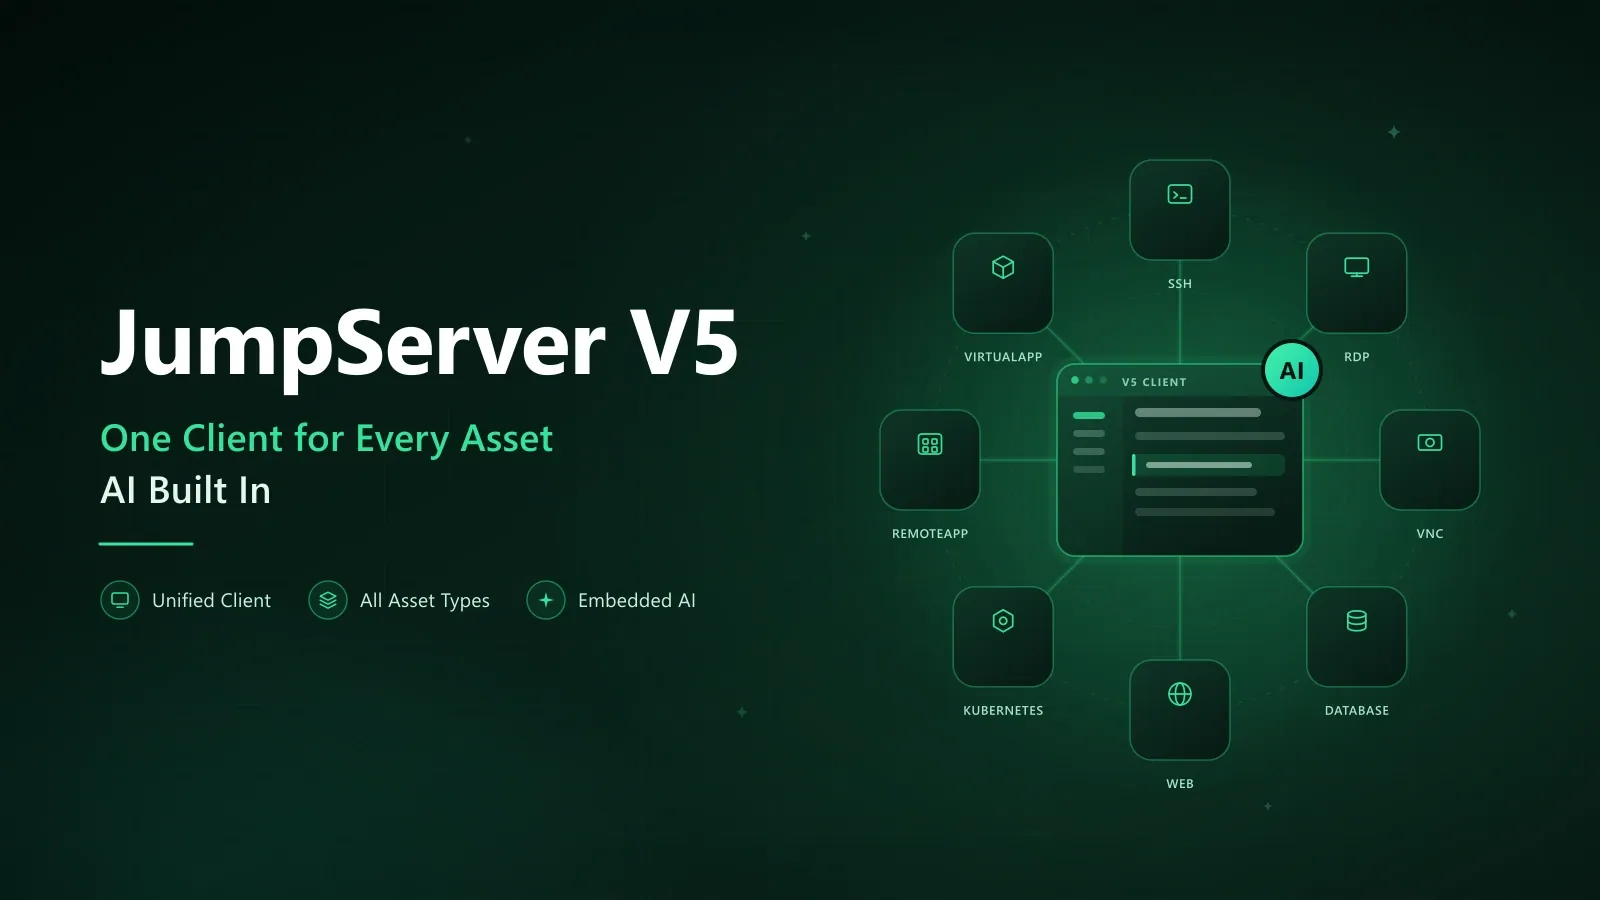
JumpServer v5.0.0 has arrived. V5 delivers a rebuilt native client that reaches SSH, RDP, VNC, databases, Web sites, Kubernetes, RemoteApp, and VirtualApp through one interface, and embeds AI in the bastion host for command recommendations, risk alerts, and automated audit reports.
A step-by-step guide to managing AWS IAM accounts and opening the AWS Management Console through JumpServer, with automated account discovery, password rotation, and verification on a custom AWS Console platform.
What is BeyondTrust? A guide to its identity security platform, product portfolio and limits, plus how JumpServer compares as an open-source PAM alternative.
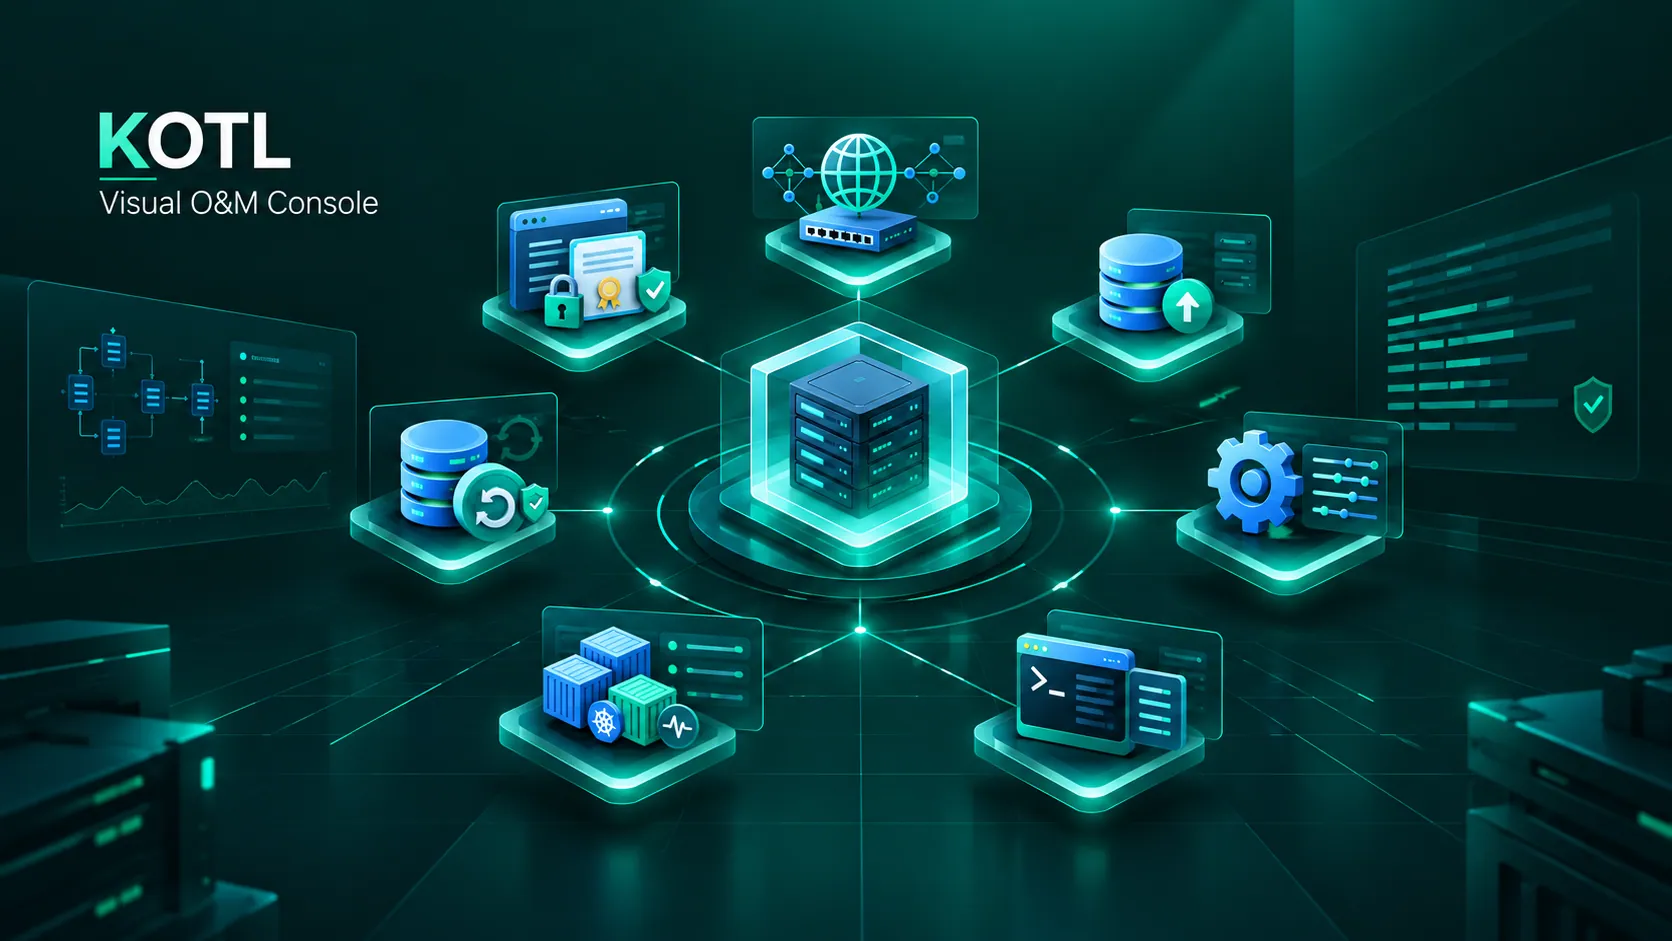
KOTL is a new component shipped in JumpServer v4.10.19 LTS that gives administrators a built-in visual console for operating and maintaining the JumpServer platform itself, from network, domain, and disk settings to encrypted backups, container lifecycle, and live application logs.
JumpServer security advisory JS-2026.09.09: an improper API filtering vulnerability (GHSA-6rp5-ff2m-qfrm, High, CVSS 8.8) lets any authenticated user retrieve administrator Access Keys by appending a query parameter. Affects V3 >= v3.7.0 and < v3.10.23 LTS, and V4 >= v4.0.0 and < v4.10.19 LTS. Upgrade or apply the Nginx workaround immediately.
Learn how Codex and JumpServer Skills turn plain-language requests into audited, least-privilege server automation, from Zabbix Agent deployment and routine inspection to alert triage and daily ops reports.
JumpServer v4.10.19-lts released: KOTL component for visualized ops, Magnus port consolidation with auto protocol detection, clipboard access control for RDP/VNC, account policy for file transfers, SMTP CA support, Chen SQL parser upgrade, Elasticsearch 9 support, and 14 bug fixes.
JumpServer security advisory JS-2026.7.29: Four vulnerabilities identified — CVE-2026-16723 (Fastjson in Chen), CVE-2026-54336 (KoKo SFTP path traversal), CVE-2026-44845 (Applet Host Jinja template injection RCE), CVE-2026-44846 (organization invitation permission override). Affects V3 < v3.10.22 LTS and V4 < v4.10.17 LTS. Upgrade to safe versions immediately.